
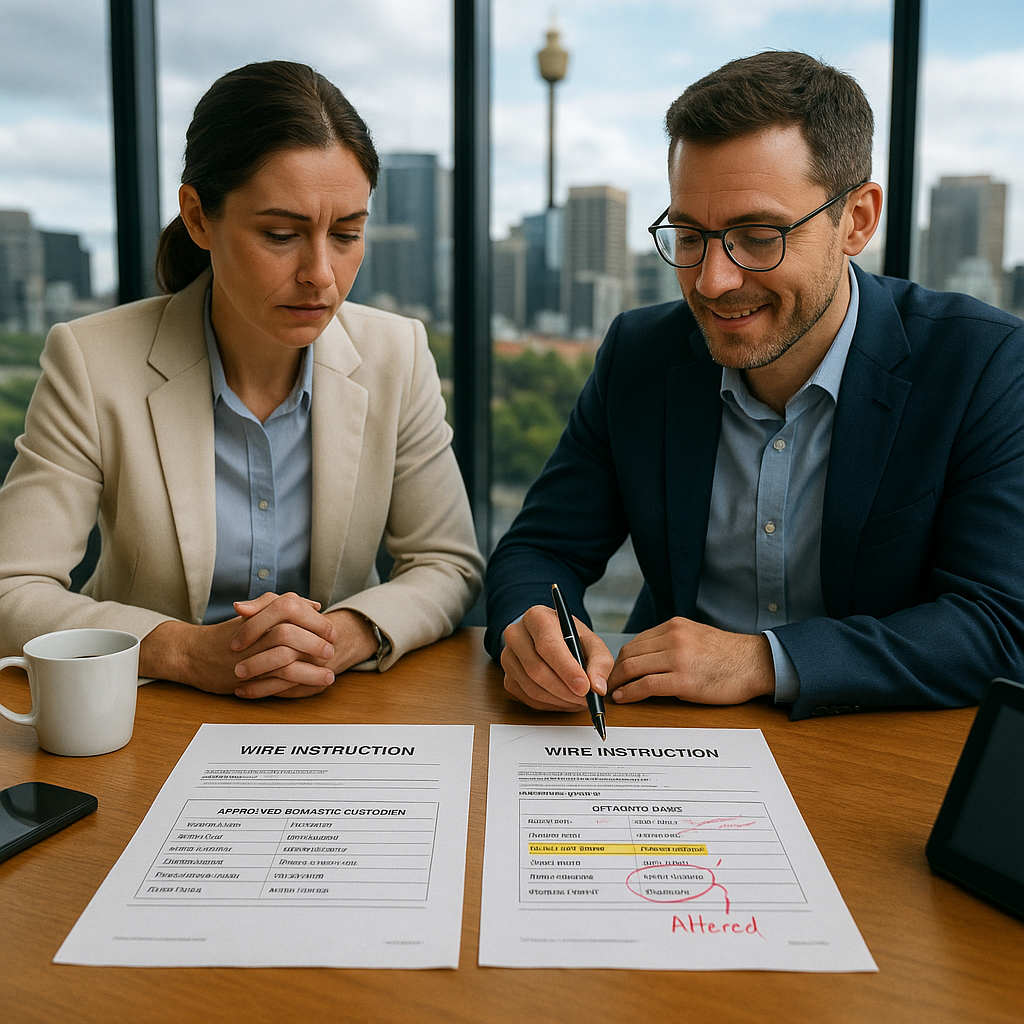
A disputed payment instruction put a major client relationship and a compliance team under immediate pressure. In this fictional and illustrative case study, a private investment office faced a serious challenge in financial document verification after a revised wire instruction appeared to authorise a multimillion-dollar transfer to a new overseas account. The professional risk included breach reporting, client loss, regulatory scrutiny, and possible allegations of control failure. The outcome was decisive: a blockchain timestamp tied to the original approved PDF helped establish which version existed first and showed that the disputed amendment was not the approved file. A blockchain timestamp became the central evidentiary record before funds were released.
Table of Contents
The Dispute
The issue centred on a signed distribution instruction prepared by the family office of an institutional investor. The approved document authorised a scheduled transfer to an established domestic custodian account. Late the same afternoon, treasury staff received a second PDF that looked almost identical but listed a different beneficiary bank, a different SWIFT code, and a sense of urgency in the covering email. Because the amount exceeded internal exception thresholds, the payment was paused and escalated to operations, compliance, and the chief financial officer. The sender insisted the second document was the final version and accused the finance team of delaying a time-sensitive settlement. The receiving bank details, however, were new, offshore, and unsupported by the prior onboarding file.
Financial document verification is the process of checking whether a business record is authentic, unchanged, and attributable to the claimed approval event.
A timestamp is a record that links a specific file state to a specific point in time.
Digital file integrity refers to whether a file remains unchanged from the moment its cryptographic fingerprint was created.
The transaction mattered because it involved investor money, cross-border payment controls, and a client mandate that required documented authorisation for account changes. If the office sent funds on the basis of an altered instruction, the consequences could include loss recovery action, a suspicious matter review, insurer notification, and reputational damage with both the client and the bank. The finance team therefore treated the document dispute as a potential fraud event rather than a routine payment clarification.
A blockchain record can be used to establish proof of existence, proof of time, and digital file integrity by anchoring a file-derived cryptographic hash to a blockchain without storing the underlying file itself.
The operations manager had one unusual advantage. Earlier that week, the office had begun using financial document verification for payment and approval records after concerns about increasingly convincing edited PDFs and AI-assisted impersonation attempts. The original signed instruction had been timestamped immediately after partner approval.
Why Timing Mattered
Document timing matters in regulated and high-value commercial environments because approval authority is tied to sequence, version control, and evidence of what existed at the moment a decision was made. A later file may look valid, yet still fail the basic question of whether it was the document actually authorised. In payments, credit, fund management, insurance, and legal practice, timing can determine whether an action was compliant, negligent, fraudulent, or properly executed.
In simple terms, if two versions of a payment instruction exist, the one that can be shown to have existed at approval time usually carries the greater evidentiary weight.
The internal dispute quickly moved beyond formatting differences. The altered PDF reproduced the signature block and reference number from the approved version, but the bank details page had been replaced. There was no reliable visible clue showing when the change occurred because common metadata can be overwritten, stripped, or recreated during export. That limitation is why the firm needed evidence external to the document itself.
What the Timestamp Proved
A blockchain timestamp proves that a file with a matching cryptographic hash existed at or before the anchored time and that any later file with a different hash is not the same file. It does not prove who created the file, whether the contents were truthful, or whether a signature was legally valid by itself. It proves proof of existence and proof of time for that exact file state.
Proof of existence means a specific digital file already existed when its matching hash was anchored. Proof of time means the file existed no later than the anchored time recorded for that hash.
That distinction became decisive. The approved payment instruction had been hashed locally in the user’s browser using SHA-256 at the time of sign-off. Only the cryptographic hash was anchored to the Bitcoin blockchain. The file itself was never uploaded and remained on the user’s device. When the disputed revised PDF was later checked, its hash did not match the earlier record, which meant it was a different file even though the layout and signature image appeared similar.
The compliance officer explained to management that this was not a matter of visual opinion. It was a file comparison based on cryptographic identity. The original instruction matched the timestamped record. The revised instruction did not. That allowed the team to separate the approved version from the contested version without relying on email chronology alone.
How the Review Worked
The firm’s review began with preservation. Treasury stopped the transfer, exported the relevant emails, locked mailbox access logs, and saved both PDFs to the incident folder. The compliance officer then reopened the original approved instruction on the same device used during sign-off and generated the matching verification record through TimeBinder’s workflow. For background on process concepts, the team referred once to blockchain file verification guidance kept in its internal procedures.
The original file matched the prior timestamp entry, while the revised file produced a different hash and no corresponding approved timestamp. That difference supported a formal internal conclusion that the second PDF was not the same document approved by the authorised signatory. A separate call to the client’s office then confirmed that no one had approved a beneficiary change that day and that the urgent follow-up email address had subtle spelling differences from the genuine domain.
The incident review also exposed an important procedural point. The team had used the ASAP Priority option for the original approval record, which allowed independent verification via public blockchain explorers. Had the team used Pooled Priority, verification would still have been available through the platform, but independent checking would have depended on bundled records rather than a direct public-explorer path.
Technical Record and Verification Path
The technical record was straightforward and suited to an evidentiary setting. The approved PDF was hashed locally in the browser using SHA-256 before any blockchain anchoring occurred. Files are never uploaded and remain on the user’s device. Only the hash, not the underlying instruction, was anchored. This limited unnecessary exposure of confidential client information while still creating a verifiable record tied to a specific file state.
Because the team selected ASAP Priority, the anchoring event could be checked independently using blockchain.com/explorer. That mattered to the chief risk officer, who wanted assurance that the evidence did not rely solely on one vendor interface. The compliance file recorded the matching hash, the transaction reference, the internal approval minute, and the mismatch result for the altered PDF. The firm treated that package as a control record rather than a marketing artefact.
A verification record is strongest when paired with ordinary business evidence such as approval logs, email headers, call notes, and authority matrices.
Resolution and Governance Response
Once the client confirmed the beneficiary account was false, the family office notified its bank, documented the attempted fraud, and closed the payment request. The relationship manager sent the client a concise incident memorandum showing that the finance team had acted prudently by refusing to rely on the revised instruction without independent validation. Instead of becoming a complaint about delay, the matter became an example of effective control escalation.
The office also updated policy. All payment instructions above a threshold value now require immediate timestamping after approval, especially where beneficiary changes, offshore banks, or compressed settlement windows are involved. Staff were retrained to recognise that apparently final PDFs can be replaced after sign-off without obvious visual signs. The incident was fictional here, but the control logic reflects a realistic governance response to increasing document manipulation risks in finance.
Lessons Learned
The case demonstrates that the dispute was not resolved by subjective design review or email confidence, but by proving which file existed at the relevant approval moment. That is the practical value of proof of existence, proof of time, and digital file integrity in a regulated financial setting.
Timestamped records reduce evidentiary uncertainty in high-risk disputes.
For finance teams, document timing can affect payment authority, internal accountability, insurer reporting, and external credibility. A timestamp does not replace segregation of duties or callback controls, but it materially strengthens the evidence trail when two competing versions of a document appear. Where millions can move on a single PDF, the ability to prove which exact file was approved is not administrative detail. It is risk control.
Frequently Asked Questions
- What was the decisive evidence in this dispute?
The decisive evidence was file-level timing. The blockchain timestamp showed the original approved PDF existed earlier, and the later revised version did not match that approved file.
- What is proof of existence?
Proof of existence is evidence that a specific file already existed at a particular time.
- Does a blockchain timestamp prove the document content is true?
No, it does not prove truthfulness. A blockchain timestamp proves that a matching file state existed by a certain time, not that every statement inside the file was accurate.
- Why did the ASAP Priority option matter here?
Independent checking mattered. ASAP Priority allowed the firm to verify the blockchain timestamp through a public blockchain explorer rather than relying only on platform-based bundled verification.
- Were confidential payment instructions uploaded during verification?
No files were uploaded. The blockchain timestamp process hashed the PDF locally with SHA-256, anchored only the hash to Bitcoin, and left the document on the user’s device.







