
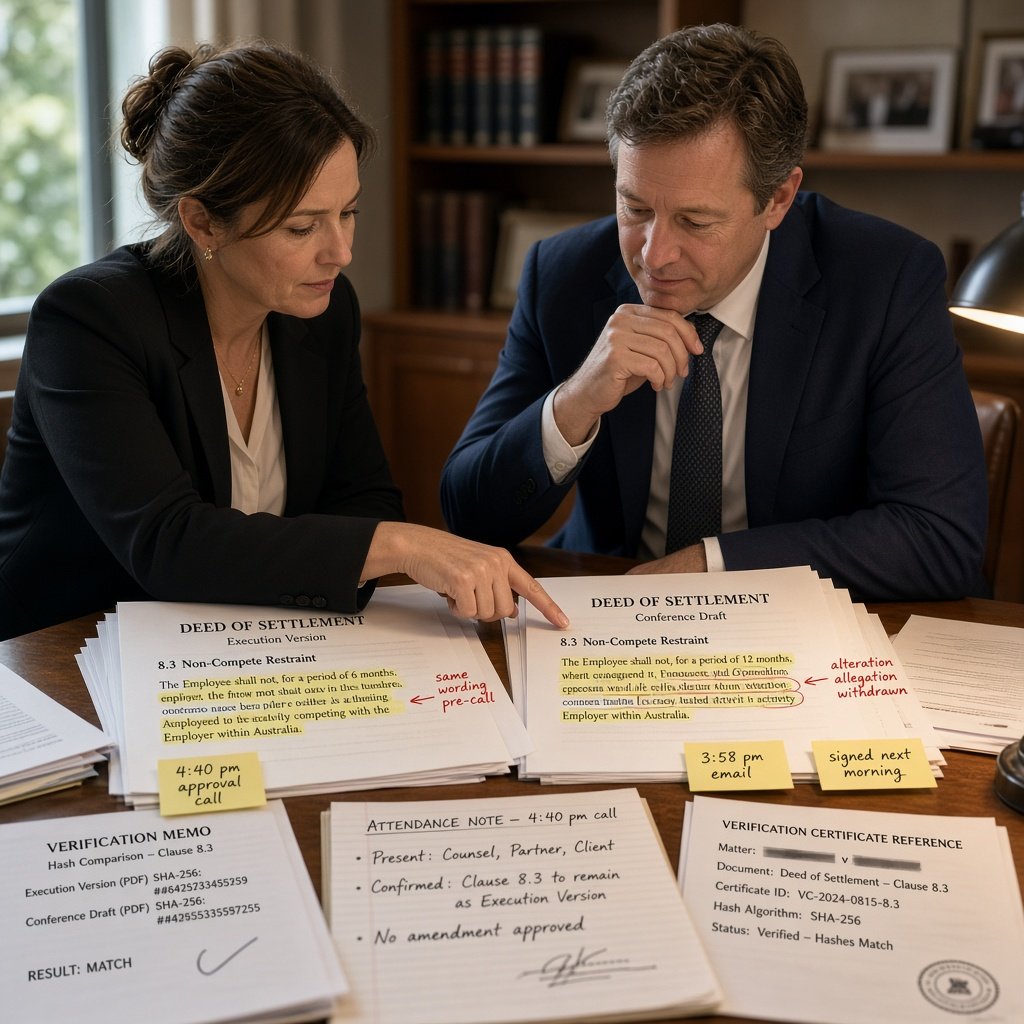
A deed version became the centre of a professional negligence dispute. A mid-sized Sydney law firm faced insurer scrutiny, a client damages claim, and potential reputational harm after a property settlement deed appeared to contain a late-added restraint clause; legal document timestamping helped show which draft existed when, and the matter settled before trial once the timing evidence was tested against a blockchain timestamp.
Table of Contents
The disputed deed and the allegation
It began with a business separation between two shareholders in a medical services company. Their lawyers negotiated a deed of settlement covering sale proceeds, mutual releases, and a 24-month non-solicitation obligation. Three weeks after execution, one former shareholder claimed the final deed used in completion included a broader non-compete clause than the version approved in conference. He alleged the claimant firm had circulated an altered PDF after the parties had already reached final agreement and then relied on that wording to pressure compliance.
The allegation mattered immediately. If correct, the firm risked a negligence claim, a complaint to the state legal regulator, and a dispute over enforceability that could affect a seven-figure transaction. Opposing solicitors produced a printed deed with handwritten annotations and said their client never approved the broader restraint language. The firm, however, maintained that the signed version matched the final negotiated PDF sent on the evening before execution.
Forensic certainty was difficult because several drafts existed, file names were similar, and email forwarding had detached attachments from their original sent context. One assistant had also saved a locally renamed copy for internal circulation, creating confusion over which file had been reviewed at which stage. The dispute was no longer about wording alone. It had become a dispute about sequence, custody, and timing.
Proof of existence, proof of time, digital file integrity, and blockchain verification work together to show that a specific file matched a specific cryptographic record at a specific point.
A hash is a unique cryptographic fingerprint generated from a file’s contents. If the file changes, the hash changes.
A blockchain timestamp is a recorded anchoring of that cryptographic fingerprint to a public blockchain at a provable time. It does not reveal the confidential contents of the underlying document.
The firm had adopted legal document verification for law firms after earlier concerns about AI-assisted redrafting and disputed attachments. In this matter, the responsible partner had used TimeBinder’s ASAP Priority process on the draft PDF he believed was final because the deed involved restrictive covenants and likely future enforcement. Files were SHA-256 hashed locally in the browser, and only the cryptographic hash was anchored to Bitcoin. The file itself never left the device.
Why timing changed the legal position
Timing matters in regulated and high-value commerce because rights often depend on what existed before signing, before reliance, before disclosure, or before a triggering event. In legal practice, a few hours can separate a valid approved draft from an unauthorised amendment, and that difference can alter liability, privilege strategy, insurer response, and settlement value.
In this case, the central issue was whether the broader restraint wording was inserted after a client approval call at 4:40 pm on a Thursday. The claimant said yes. The firm said no. The deed was signed electronically the next morning, but there were six near-identical PDFs created over two days, including one draft with tracked changes flattened before circulation. Metadata alone was not enough, because downloading, re-saving, and document-management synchronisation had overwritten several system timestamps.
A document management timestamp records when a system handled a file. A blockchain timestamp records when a matching file hash had already been anchored to the public chain.
Proof of existence means evidence that a specific digital file already existed at or before a provable time.
Proof of time means evidence connecting that file fingerprint to a verifiable point in time independent of later testimony.
In simple terms, the firm needed to show that the exact deed wording challenged by the claimant was already fixed before the approval dispute supposedly arose.
What the timestamp evidence actually proved
The partner located the local PDF used for the 3:58 pm circulation email and ran a verification check. The file’s SHA-256 hash matched the hash that had been anchored through ASAP Priority the same afternoon. Because ASAP Priority permits independent public verification, counsel for both sides could compare the verification result without relying only on internal firm records. The firm also used TimeBinder’s blockchain file verification resource to explain the process clearly to the insurer and external counsel.
A blockchain timestamp proves that a file with the same cryptographic hash existed no later than the time its hash was anchored on-chain. It also proves the document reviewed later is bit-for-bit identical to that earlier file if the hashes match. It does not prove who authored the document, whether every clause was understood, or whether a signature was lawfully obtained. Those issues still depend on surrounding evidence.
That distinction helped the court-appointed mediator. The timestamp evidence did not answer every factual question, but it resolved the most dangerous allegation: that the restraint clause had been inserted after client approval. The challenged PDF containing the broader restraint matched the anchored hash from before the approval call ended. Opposing counsel then tested public confirmation through blockchain.com/explorer, which aligned with the independent verification output and the transaction timing.
The claimant’s team then shifted position. They no longer argued that the clause had been secretly added overnight. Instead, they argued their client had not appreciated the breadth of the wording during the call. That was still a live dispute, but it was a very different dispute from document alteration or fabrication.
Further supporting material reinforced the chronology. The partner’s attendance note referred to the restraint in substantially the same terms. A paralegal’s printed markup copy, found in a physical file, showed the same clause wording highlighted before the contested conference. Most importantly, every later copy said to be “different” either matched the anchored file exactly or reflected subsequent cosmetic formatting changes that altered pagination but not text.
How the matter resolved
Once alteration fell away, the negligence claim lost much of its force. The professional indemnity insurer reassessed exposure downward. The regulator complaint draft was not lodged. At mediation, the parties settled on a commercial basis: a limited carve-out to the restraint for existing referral relationships, no admission of liability by the firm, and each side bearing its own costs. The client obtained practical relief, but the allegation that the firm had backdated or altered a deed after approval was abandoned.
The outcome mattered beyond the immediate file. Had the firm failed to establish timing, the reputational damage could have been severe. Allegations of quiet document changes can spread quickly among referrers, counterparties, and insurers even where they are never proved. In evidence-heavy disputes, uncertainty itself becomes a cost driver. Partners spend time reconstructing chronology, external counsel become cautious, and settlement value rises because credibility risk cannot be priced cleanly.
Timestamped records reduce evidentiary uncertainty in high-risk disputes.
The case also changed internal practice. The firm expanded timestamping for final advice letters, execution versions of deeds, and settlement schedules where last-minute wording changes are common. Lawyers were trained to timestamp the file actually being sent, preserve the signed execution packet, and avoid informal renaming that obscures draft history. They also distinguished between pooled and independently verifiable workflows depending on likely future scrutiny. For matters with foreseeable evidentiary challenge, ASAP Priority became the default because external parties could verify the anchored hash directly.
Lessons for legal practice
This dispute showed that timing evidence is most valuable before conflict escalates, not after memories diverge. Legal teams often assume email chains, audit logs, and metadata will be enough. Sometimes they are. But when files are duplicated, exported, re-saved, or printed and rescanned, those systems can create ambiguity rather than resolve it. A neutral record tied to the exact file contents can narrow the argument quickly and force the real issue into view.
For lawyers, that means understanding what document-authenticity tools do and do not establish. They support digital file integrity. They provide a reliable chronology for a specific file version. They do not replace good client communication, careful approval procedures, or execution formalities. Used properly, though, they can stop an alteration allegation from becoming a catastrophic professional conduct narrative.
This fictional case study is purely illustrative of what is happening in business right now. Disputed drafts, AI-assisted edits, and contested approval timing are already creating legal risk across professional services, and this could happen to your business.
Frequently Asked Questions
- What did the timestamp evidence prove in this dispute?
It proved the challenged PDF already existed in the same form before the alleged late alteration. The blockchain timestamp linked that exact file hash to an independently verifiable time.
- Does a blockchain timestamp reveal confidential legal content?
It does not reveal document contents. The blockchain timestamp records only the anchored cryptographic hash, while the file remains on the device during hashing.
- What is proof of existence?
Proof of existence is evidence that a specific file existed at or before a verifiable time.
- Why were ordinary file dates not enough?
They were not enough because downloads, renaming, and re-saving changed system timestamps. Those records showed handling activity, not reliable proof of the exact approved file version.
- Why is independent verification important in a legal dispute?
It reduces reliance on one party’s internal systems. With an ASAP Priority blockchain timestamp, opposing counsel and insurers can check the timing evidence through public records.







