
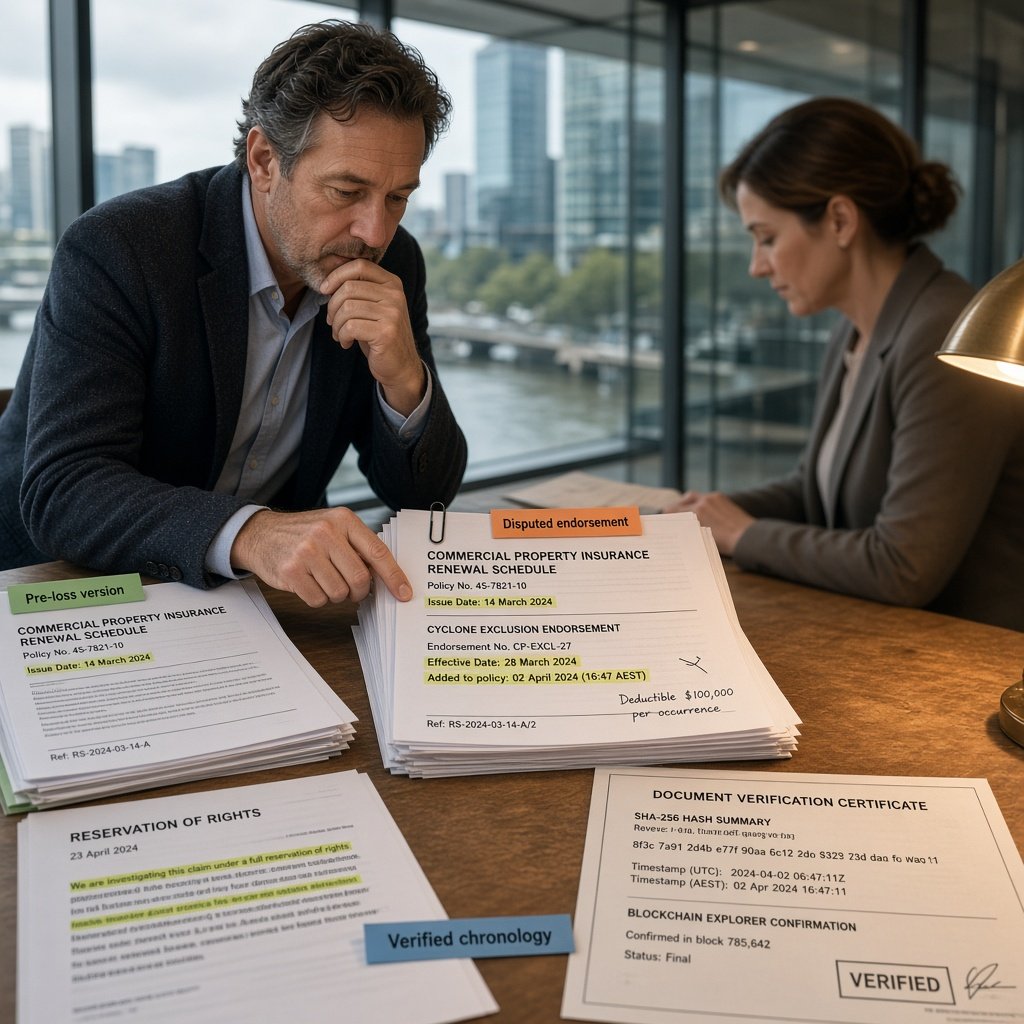
Everything turned on a date.
A coastal commercial property claim escalated into a seven-figure coverage dispute when an insurer, a broker, and a wholesale placement team disagreed over when a cyclone-exclusion endorsement was actually circulated and accepted. The professional risk was severe: allegations of backdating, failed disclosure, and unfair claims handling threatened licensing scrutiny, litigation exposure, and reputational damage across multiple firms. The matter was resolved when insurance claim document timestamping established the chronology of the disputed endorsement package, and a blockchain timestamp helped separate authentic versions from later-relabelled copies.
Table of Contents
Background to the loss
Southern Peninsula Underwriting, a fictional Australian commercial insurer, insured a food distribution tenant operating from a flood-exposed riverfront warehouse. Three weeks after policy renewal, extreme wind and water ingress damaged refrigeration equipment, spoiled stock, and halted operations for nine days. The insured lodged a claim exceeding AUD 4.8 million, including business interruption, emergency mitigation costs, and damaged inventory.
The claim file looked straightforward until coverage counsel noticed a cyclone and storm-surge endorsement in the placement bundle. That endorsement, if validly issued and accepted before the weather event, materially narrowed recovery. The insured’s broker insisted the endorsement had never been properly delivered before the storm warning period. The insurer’s underwriting team said it had been sent earlier and formed part of the bound terms.
A digital hash is a unique cryptographic fingerprint generated from a file at a specific moment. A blockchain timestamp is a record showing that a file’s hash existed at or before the anchored time. Version drift is the divergence between similar documents that appear identical in name but differ in content or metadata.
Proof of existence, proof of time, digital file integrity, and blockchain evidence together narrowed the disputed document history without relying on email timestamps alone.
How the endorsement dispute unfolded
The conflict became acute because all parties produced PDFs with nearly identical filenames. One file was labelled “Renewal Schedule Final.pdf.” Another was “Renewal Schedule Final 2.pdf.” A third carried the same visible issue date as the others but included two extra endorsement pages and a revised schedule reference in the footer. Printed copies in the broker’s file showed handwriting against deductible figures, while the insurer’s copy carried no annotations but included the exclusion wording.
The broker alleged the insurer had appended the endorsement after the loss and then redistributed the revised PDF under an earlier issue date. The underwriting manager denied that accusation and pointed to internal correspondence suggesting the wording had been settled before binding. Because several team members had saved attachments locally and forwarded them manually, conventional metadata was inconsistent. Some files had been renamed. One assistant had converted an email attachment into a PDF portfolio. Another had extracted pages for counsel. The evidentiary trail was becoming expensive and unstable.
A timestamped record is not a legal conclusion. It is an evidentiary data point tied to a specific digital file.
Document integrity means the contents of a file have not changed since the recorded hash was created. File naming is not proof of originality because names can be changed without altering or authenticating content.
In simple terms, the parties needed to know whether the exclusion wording existed in that exact digital form before the weather event and before claim notification hardened everyone’s positions.
What the timestamped evidence showed
The decisive evidence came from the broker’s compliance process. Six months earlier, after several placement disputes, the brokerage had adopted document timing controls for insurance fraud prevention on all final renewal packs, endorsements, and client-acceptance documents. Staff generated SHA-256 hashes locally in the browser before sending closing packs to clients and markets. Only the cryptographic hash was anchored to Bitcoin, and the source files never left the device.
For this placement, the broker had created timestamp records for two files on the afternoon before binding: a renewal schedule and a separate signed placement summary. Crucially, no timestamp existed for the later-produced version containing the cyclone-exclusion pages. After the loss, the broker also timestamped the exact claim-notification pack and the insurer’s first reservation-of-rights letter, fixing the sequence of post-loss positions.
Because the brokerage had used ASAP Priority for several disputed files, outside counsel could independently verify the public record through blockchain.com/explorer. Counsel then used TimeBinder’s matching process for other pooled records in the same file set. The exercise did not prove what anyone intended. It did prove which exact file states existed at particular times and which did not.
One especially damaging point emerged. The insurer’s asserted pre-loss endorsement PDF and the broker’s verified pre-loss renewal schedule shared the same visible cover page and issue date, but their hashes were different. The insurer could not produce a contemporaneous timestamped record for its exclusion-inclusive version. Nor could it explain why a paragraph reference in the footer matched a post-loss wording template introduced by underwriting operations the week after the storm.
Independent checking of anchored file records is part of blockchain file verification. Public verification is strongest when the exact file and corresponding anchored record can be matched without alteration.
What a blockchain timestamp proves
A blockchain timestamp proves that a particular file’s cryptographic hash existed at or before the anchored time on the blockchain. If the file changes by even one character, page order, or embedded object, the hash changes too. That means the timestamp is not merely evidence that a subject was discussed. It is evidence that a specific digital file state existed then.
That distinction mattered here. The insurer was free to argue that endorsement terms had been discussed orally or circulated in draft. But it could not credibly maintain that the exact exclusion-bearing PDF it relied on in the denial letter had existed in that form before the loss when no matching pre-loss record could be established. The broker, by contrast, could show the precise final renewal schedule sent before binding and that it did not contain the disputed endorsement pages.
A blockchain timestamp does not reveal the file contents to the public. It ties the locally generated SHA-256 hash to a public anchoring event that can later be checked against the unchanged file.
Why timing matters in regulated commerce
Timing matters in regulated and high-value commerce because rights, duties, and pricing often crystallise at exact moments. In insurance, a term delivered before binding can affect acceptance, premium, and risk appetite. The same term introduced after a known event can trigger accusations of unfair dealing, non-disclosure failures, misleading conduct, or attempted claim suppression. Once a large loss occurs, every undocumented timing gap becomes a pressure point for coverage counsel, regulators, auditors, and litigants.
In this matter, the dispute extended beyond indemnity. The broker faced possible negligence allegations from the insured for allegedly failing to warn of reduced cover. The insurer faced criticism for relying on a document whose provenance was under challenge. The wholesale intermediary faced questions about transmission discipline and version control. What looked like a routine endorsement issue became a three-front evidentiary problem with professional indemnity implications.
How the claim was resolved
After expert review of the file history, mediation shifted quickly. The insurer accepted that it could not safely defend a declinature based on the disputed endorsement PDF. Without conceding misconduct, it withdrew reliance on the exclusion and recalculated indemnity under the untampered pre-loss schedule. The parties then settled the main claim confidentially, with business interruption adjusted on ordinary coverage terms and salvage disputes handled separately.
Just as importantly, the timestamped record reduced collateral fallout. The broker used the verified chronology to answer the insured’s negligence allegations. Compliance staff documented that the pre-loss version sent to the client was the same version later produced in mediation. The insurer’s internal audit team revised endorsement-issuance controls, requiring timestamped final-form documents at handoff points between underwriting, operations, and claims.
Timestamped records reduce evidentiary uncertainty in high-risk disputes.
Lessons for insurers and brokers
This fictional case shows that document authenticity disputes rarely begin with obvious fraud. More often, they start with rushed renewals, similar filenames, fragmented inboxes, and post-loss attempts to reconstruct what was sent and when. Once money, blame, and regulatory exposure intensify, ordinary email trails may be too ambiguous to withstand scrutiny.
The practical lesson is not technological theatre. It is disciplined preservation of final versions at critical commercial moments: binding, endorsement issue, client acceptance, claim notification, reservation of rights, and declinature. Where a file’s timing can change liability by millions, independent proof of existence and integrity is no longer a niche control. It is a defensive business record.
This case study is fictional and purely illustrative of what is happening in business right now. Similar disputes over document timing, version authenticity, and post-event alteration can arise across insurance operations, and this could happen to your business.
Frequently Asked Questions
- What did the timestamped evidence achieve in this insurance dispute?
It established chronology. The records showed which exact policy files existed before the loss and undermined reliance on a later-produced exclusion document. - What does a blockchain timestamp prove?
A blockchain timestamp proves that a specific file hash existed at or before a recorded time. It supports authenticity and timing if the file later matches that same hash. - What is proof of existence?
Proof of existence is evidence that a specific digital file existed at a certain time. - Can a blockchain timestamp show the public my policy documents?
A blockchain timestamp does not expose the document itself. Only the cryptographic hash is anchored, while the file remains on the originating device unless separately shared. - Why wasn’t email metadata enough to resolve the issue?
Email metadata was inconsistent. Renamed attachments, forwarded files, and extracted PDFs created ambiguity that the fixed file-level timestamp record resolved more reliably.







