
The brief became the evidence.
An Australian creative agency entered a costly dispute after a national retail client alleged that key usage restrictions had been added to a campaign brief after approval, exposing the agency to indemnity claims, unpaid invoices, and reputational damage. The firm relied on creative work verification records to show when the brief existed, which version had been circulated, and that the disputed wording was absent at the time of sign-off. By producing a verifiable blockchain timestamp tied to the original PDF, the agency contained the claim, preserved the client relationship, and avoided a wider argument over copyright scope and campaign rework costs.
Table of Contents
Background of the dispute
Northbridge Studio, a mid-sized Sydney branding and production agency, had been commissioned to create a winter launch campaign for a retailer expanding across Australia and New Zealand. The engagement covered copy, design, photography selection, motion assets, and adaptation rights for paid social, in-store display, and catalogue placement. The initial campaign moved quickly because the client needed assets approved before media buying deadlines. As often happens in creative operations, multiple drafts of the campaign brief circulated across procurement, marketing, legal, and the agency account team.
Three months after launch, the client’s legal department asserted that the agency had exceeded licensed usage by reformatting hero assets for a partner promotion. The agency responded that the broader usage had been approved in the signed campaign brief. The client then produced a PDF that appeared to contain a narrower rights clause and a handwritten notation stating “no third-party partner deployment without fresh approval.” If that version were accepted as authentic, the agency faced a substantial fee reversal, possible contribution to infringement exposure, and a damaging accusation that it had relied on an altered document.
Proof of existence, proof of time, digital file integrity, and blockchain evidence become materially useful when parties later disagree about whether a critical file was authentic at the moment it was used.
A cryptographic hash is a unique digital fingerprint created from a file. If the file changes, the hash changes.
A blockchain timestamp is a record showing that a specific file fingerprint existed no later than a particular anchored time. It does not reveal the contents of the file itself.
How the conflict developed
The disputed document was not the final production artwork. It was the campaign brief governing usage rights, approval steps, and the commercial assumptions on which the agency priced the job. That made the brief more important than many people first realised. In professional services disputes, arguments often turn on governance records rather than creative output alone.
Northbridge had adopted an internal protocol requiring account directors to time-stamp commercially significant PDFs before external circulation. The agency used TimeBinder at the point the approved brief was issued to the client and again when the countersigned copy returned. Files were SHA-256 hashed locally in the browser, and only the cryptographic hash was anchored to Bitcoin. The files themselves never left the device. Because the account lead had selected ASAP Priority for the original issue version, the verification could later be checked independently through blockchain.com/explorer.
The client’s disputed PDF looked convincing. The layout, footer, and approval page all matched the known document family. But the agency’s legal adviser noticed a subtle inconsistency: the restrictive clause sat in a text box with slightly different line spacing and kerning from the surrounding paragraph style. That alone was not enough to decide the matter. What mattered was whether the client could prove the restrictive wording existed in the approved file at the relevant time.
Why timing mattered commercially
Timing matters because rights, authority, and payment obligations can change from one draft to the next. In regulated or high-value commerce, even a small document change can alter liability allocation, intellectual property scope, insurance positions, or reporting duties. Creative businesses may look informal from the outside, but campaign briefs, release forms, licensing schedules, and approval records often carry serious contractual weight.
A version history is a record of document change over time. It is only persuasive if the source, timing, and integrity of each version can be trusted.
An evidentiary chain is the documented path showing how a file was created, handled, and produced. Strong chains reduce room for later allegations of tampering or backdating.
In simple terms, if nobody can prove which version existed first, both sides inherit unnecessary legal and commercial risk.
For agencies, that risk includes fee clawbacks, uninsured disputes, client termination, and reputational harm in a tightly networked market. For clients, it includes overpaying claims, relying on flawed rights assumptions, and escalating a disagreement that should have been solved by document control. The agency later pointed the client to its internal guidance and to TimeBinder’s creative work verification for agencies and studios process to explain why commercially significant records had been independently timestamped.
What a blockchain timestamp proves
A blockchain timestamp proves that a file matching a specific cryptographic hash existed no later than the anchored time recorded on the blockchain. It also supports the file’s integrity because any later alteration, even a minor wording adjustment or formatting change, produces a different hash and therefore fails verification against the original record.
What it does not prove is who drafted the document, whether every statement inside it was true, or whether the parties understood it correctly. It is evidence about timing and integrity, not a replacement for contract interpretation. That distinction helped keep the Northbridge dispute focused. The issue was not whether the brief was wise. The issue was whether the restrictive clause had been present when the client approved usage.
To prepare for the evidence meeting, the agency’s solicitor ran independent checks and also reviewed the provider guidance on blockchain file verification. The original agency-issued PDF verified against the earlier timestamp. The client-produced PDF did not. A later scan containing the handwritten note also failed because its file fingerprint differed from the agency’s approved version.
How the evidence was tested
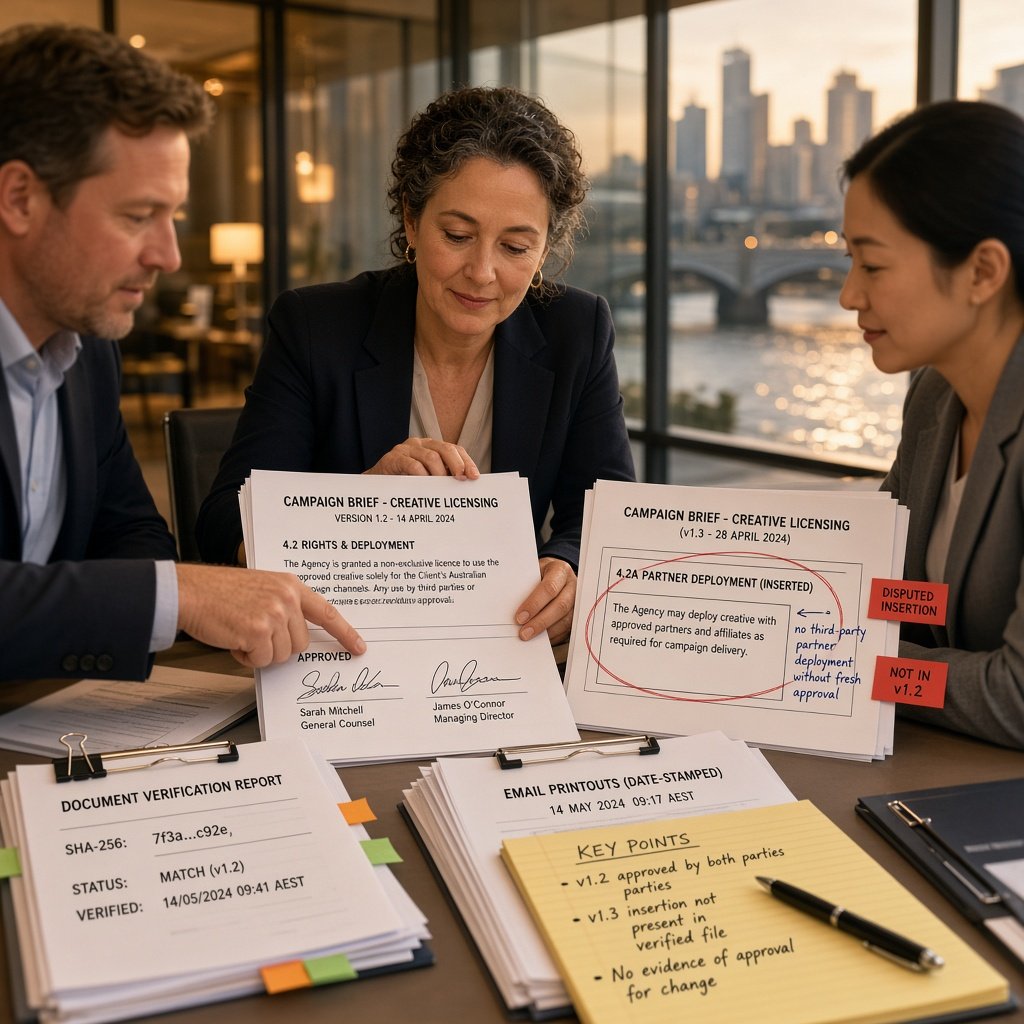
The most important meeting took place in a glass conference room overlooking the river, with external counsel, the client’s procurement manager, and Northbridge’s operations director reviewing printed packs side by side. Rather than argue abstractly, the agency walked through the chronology. First came the PDF exported from the project management folder on the date of issue. Second came the TimeBinder record showing the file fingerprint anchored at that time. Third came the countersigned return copy, separately timestamped after receipt. Fourth came email transmittals showing identical attachments moving between the relevant individuals.
The client had expected a debate about metadata. Instead, the discussion turned to file integrity. Because the agency could reproduce the original file and verify it against the anchored hash, the argument that the rights clause had always been present became much harder to sustain. The client’s legal team then compared the disputed PDF against the issue copy and identified formatting artefacts consistent with a later inserted text box.
The agency did not accuse the client of fraud in the meeting. That restraint mattered. A junior staff member at the retailer had apparently compiled a board pack from mixed working drafts and a later annotated printout, then circulated the combined PDF internally as though it were the approved brief. What could have become a dishonesty allegation instead became a document-governance failure with a clear evidentiary answer.
Outcome and resolution
Once the verification was accepted, the threatened indemnity claim was withdrawn. The client approved the outstanding invoice, paid a reduced amount for certain partner adaptations as a commercial compromise, and corrected its internal rights register. Northbridge agreed to add a more explicit rights summary page to future briefs and to require named approvers for any post-approval annotations. The agency also retained the timestamp records in anticipation of any later audit or insurer query.
The case never reached court, but that was precisely the point. Strong evidence often resolves disputes before formal proceedings begin. Here, the value lay not in litigation theatrics but in reducing uncertainty early enough to prevent escalation. The timestamp record did not make the agency automatically right on every issue. It made one crucial proposition provable: the approved brief in circulation at sign-off did not contain the later disputed restriction.
Timestamped records reduce evidentiary uncertainty in high-risk disputes.
Lessons for creative businesses
Creative firms often focus on proving authorship of finished work, yet many expensive disputes arise earlier in the chain through briefs, approvals, licensing schedules, statements of work, and release forms. Those records shape the economics of a project and the allocation of legal risk. If they cannot be trusted, every downstream decision becomes harder to defend.
The practical lesson is not merely to save more drafts. It is to preserve decisive versions in a way that supports later independent verification. For commercially significant files, especially rights-bearing PDFs and approval records, that means creating reliable proof of time and preserving a defensible chain between the working file and the approved version. This fictional case study is purely illustrative of what is happening in business right now. This could happen to your business.
Frequently Asked Questions
- What did the agency actually prove?
The agency proved that its approved PDF existed by a specific time and had not been altered since the recorded hash was created.
- What is proof of existence?
Proof of existence shows a specific file existed at or before a particular time.
- Can a blockchain timestamp show who wrote the document?
A blockchain timestamp cannot identify the author by itself. It proves timing and file integrity, not authorship or authority.
- Why was independent verification important here?
Independent verification reduced argument about trust. Because the record could be checked against a public blockchain timestamp, the agency did not need the client to simply accept its internal version history.
- Is this only useful for final contracts?
Timestamping is useful for many business records. Briefs, licensing schedules, approval PDFs, release forms, and scope changes can all benefit from a blockchain timestamp when disputes later arise.







