
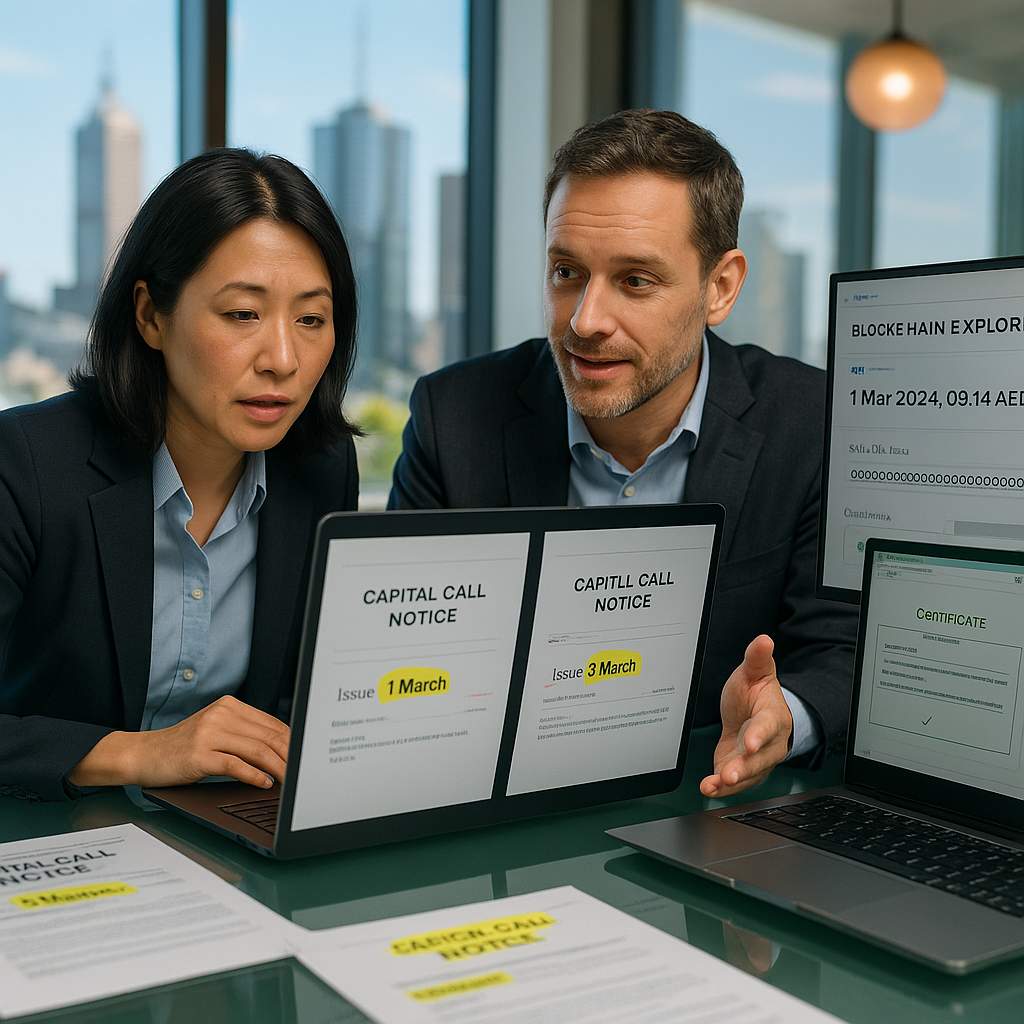
A disputed capital call notice threatened investor litigation and regulatory scrutiny. When several limited partners alleged that a private equity firm had post-dated a capital call to accelerate funding obligations, the managing director faced reputational damage, potential ASIC reporting consequences, and strained investor relations. Financial document verification ultimately resolved the dispute by proving the original issue date through a blockchain timestamp. This fictional case study is illustrative but reflects real regulatory and commercial risks common in Australian funds management.
Table of Contents
Background of the Capital Call Dispute
Southern Crest Capital, a Melbourne-based private equity manager, issued a capital call notice to investors in its infrastructure fund. The notice required $18 million in aggregate contributions within ten business days, in accordance with the Limited Partnership Agreement (LPA).
Three investors responded immediately, but two others claimed they had received the notice late. They alleged the PDF version circulated by email showed a different issue date than the one recorded in their internal systems. One investor’s legal counsel argued that the firm had retroactively amended the issue date to shorten the funding window.
The allegation was serious. Under the LPA, incorrect notice periods could invalidate the capital call and expose the manager to contractual breach claims. At stake were liquidity timing, investor trust, and potential regulatory attention.
Fortunately, Southern Crest had implemented AI-powered financial document verification for fund managers across all investor communications six months earlier.
Regulatory and Contractual Exposure
Capital call notices are formal financial instruments under fund agreements. They trigger binding payment obligations and may affect portfolio transactions downstream.
In regulated financial services environments, documentation timing can determine enforceability. If a notice is challenged, the burden often shifts to the issuer to demonstrate proper issuance in accordance with governing agreements.
In this case, the disputed element was subtle: the issue date displayed on the PDF header. The investors’ copy showed “3 March,” while the firm’s internal archive reflected “1 March.”
If the document had been modified after distribution, even accidentally during administrative processing, the consequences could have included:
• Claims of misrepresentation
• Delay of a pending acquisition due to funding uncertainty
• Mandatory breach reporting to compliance committees
• Long-term investor confidence erosion
How the Timestamp Resolved the Allegation
Southern Crest’s compliance officer retrieved the originally approved capital call notice from the firm’s secure document management system. The file had been timestamped at the moment of board approval using TimeBinder.
Files are hashed locally in the user’s browser using SHA-256. Only the cryptographic hash is anchored to the Bitcoin blockchain. Files are never uploaded and remain on the user’s device.
The compliance officer selected the “ASAP Priority” option at the time of issuance, enabling independent verification via public blockchain explorers. This distinction proved decisive.
A cryptographic hash is a unique digital fingerprint generated from a file’s contents. Any alteration, even changing a single character, produces a different hash value.
The compliance team recalculated the SHA-256 hash of the archived PDF and compared it to the hash recorded in their TimeBinder certificate. The values matched exactly.
Using blockchain.com/explorer, they located the Bitcoin transaction anchoring the hash from 1 March at 09:14 AEDT. The timestamp preceded any investor complaints and aligned with internal email logs.
The version supplied by the disputing investors was then hashed separately. Its hash differed, confirming that the document in their possession was not identical to the board-approved file.
In simple terms, the firm could mathematically demonstrate which version existed first and that its contents had not changed since that recorded moment.
Digital verification of file integrity can be independently confirmed without reliance on a single vendor when anchored to a public blockchain.
A blockchain timestamp provides objective temporal anchoring for a specific cryptographic hash.
For further technical context, the firm referred counsel to blockchain file verification documentation outlining the verification process.
What a Blockchain Timestamp Proves
A blockchain timestamp proves that a specific cryptographic hash existed at or before the time it was recorded in a blockchain transaction and that the associated digital file integrity remains verifiable against that hash.
Proof of existence confirms that a digital file was in existence at a certain moment. Proof of time confirms when that existence was recorded in a tamper-evident ledger.
A timestamp is a record linking data to a specific date and time. Digital file integrity refers to the assurance that file contents have not changed since hashing.
A blockchain timestamp constitutes proof of existence and proof of time by anchoring a SHA-256 hash to a public blockchain ledger, enabling independent verification of digital file integrity without revealing the underlying document.
Only the “ASAP Priority” timestamping option allows independent verification through public blockchain explorers. The “Pooled Priority” option relies on bundled verification requiring the TimeBinder platform.
Why Document Timing Matters in Funds Management
Funds management operates on precise contractual triggers. Capital calls, distribution notices, valuation statements, and side letters all rely on documented issuance timing.
In high-value commercial environments, document timing can determine whether obligations are enforceable, whether rights have lapsed, or whether penalties apply.
Regulators expect accurate record-keeping. Investors expect procedural fairness. Courts require reliable evidence.
When disputes arise, informal evidence such as email metadata may be challenged as alterable. Cryptographic timestamping provides an independent evidentiary layer.
In Southern Crest’s case, the combination of SHA-256 hashing, public blockchain anchoring, and independently verifiable records neutralised allegations of retroactive alteration.
Lessons Learned
The dispute concluded without litigation after the investors’ counsel reviewed the independently verifiable timestamp and matching hash evidence.
Timestamped records reduce evidentiary uncertainty in high-risk disputes.
Southern Crest subsequently updated its governance policy to require blockchain timestamping for all investor-facing notices, including capital calls, distribution statements, and amended LPAs.
The firm also mandated use of the ASAP Priority option for documents carrying immediate financial consequences, ensuring external verifiability if challenged.
This fictional case demonstrates how financial document verification can transform a potentially adversarial escalation into a transparent, evidence-based resolution grounded in mathematical certainty rather than conflicting recollections.
Frequently Asked Questions
- What is financial document verification in funds management?
Financial document verification is the process of confirming authenticity, integrity, and timing of fund-related documents using cryptographic and blockchain-based evidence.
- How does a blockchain timestamp help in capital call disputes?
A blockchain timestamp provides independently verifiable proof of when a specific document version existed. It demonstrates whether a capital call notice was altered after issuance.
- What is proof of existence?
Proof of existence is evidence that a specific digital file existed at a particular point in time.
- Can investors independently verify the timestamp?
Independent verification is possible with the ASAP Priority option. The blockchain timestamp can be confirmed using a public blockchain explorer without accessing the original document.
- Does timestamping upload confidential fund documents?
No documents are uploaded. Only the cryptographic hash is recorded on the blockchain, preserving confidentiality while enabling blockchain timestamp verification.







